Enterprise Security for Complex, Evolving Environments
AppsChopper helps enterprises strengthen security across identities, applications, infrastructure, data, and AI systems. We design, implement, and support security capabilities aligned with your risk profile, technology environment, and operational requirements across cloud, on-premises, and legacy systems.
Trusted by Fortune 500 innovators and high-growth startups
Why now
Enterprise Security Must Evolve with the Threat Landscape
Enterprise security risks are expanding beyond traditional network boundaries. Compromised credentials, excessive access privileges, fragmented monitoring, and unmanaged AI adoption create gaps across increasingly complex technology environments. Security programs must evolve to address these risks across the full enterprise.
Fragmented Security Operations
Disconnected security tools and monitoring systems can create blind spots, duplicate alerts, and inconsistent incident visibility. Without effective coordination, security teams face greater difficulty prioritizing threats and responding efficiently.
Expanding Cloud Environments
New cloud services, software-as-a-service applications, APIs, and identities increase the complexity of access control and configuration management. Misconfigured resources and excessive permissions can expose sensitive systems and data to avoidable risk.
AI Introduces New Security Requirements
Copilots, AI agents, and applications built on large language models introduce risks involving prompt injection, sensitive data exposure, unauthorized tool access, and unapproved AI usage. Enterprises need security controls and governance that account for how AI systems access data and interact with existing infrastructure.
Our services
End-to-End Enterprise Security Services. From Strategy to 24/7 Defense.
Security services designed to address enterprise risk, modernize security capabilities, and support ongoing protection across complex technology environments.
Security assessment and strategy
We run risk assessments, penetration tests, and maturity benchmarks against NIST CSF 2.0. You get a prioritized, budget-ready roadmap that your board can approve and your teams can execute.
Security architecture and design
Our enterprise security architecture consulting delivers buildable reference designs for Zero Trust, cloud, and identity. Every control maps to a risk it retires, so every dollar has a purpose.
Implementation and integration
We deploy, configure, and integrate security platforms into your existing stack without disrupting operations. Then we tune every rule and alert until your tools deliver signal, not noise.
Migration and modernization
Move off aging IAM, on-prem SIEM, or VPN to modern cloud-native platforms. Parallel runs and zero-downtime cutovers keep users working and protected through every step of the switch.
DevSecOps and application security
We build SAST, DAST, SCA, and secrets scanning directly into your CI/CD pipelines. Developers fix vulnerabilities in the pull request, not in production, and releases keep their pace.
Managed security services
Our security operations center as a service runs fully managed or co-managed, under defined SLAs. A named team learns your environment, hunts threats daily, and reports to executives monthly.
Incident response and recovery
We set up response retainers, tabletop exercises, forensics, and ransomware recovery playbooks. When incidents hit, your first call goes to a team that already knows your environment.
Security awareness and training
We run phishing simulations, role-based training, and executive tabletop drills tailored to the threats your industry faces. Your employees become sensors that report attacks, not entry points for them.
Strengthen Your Enterprise Security Posture
Identify security priorities and determine where improved controls, architecture, and operational practices can make the greatest difference.
Security capabilities designed to address risk across identities, privileged access, infrastructure, applications, data, and AI systems. Each layer supports a coordinated security strategy aligned with your technology environment, operational requirements, and risk priorities.
Layer 01 · Identity & Access
Identity and Access Management Services
We deploy and modernize single sign-on, adaptive MFA, and automated lifecycle provisioning across your workforce, partners, and customers. Auditors get a clean trail every time.
What’s included
Workforce and customer identity (CIAM) on Okta, Microsoft Entra ID, Ping, or your existing stack
Single sign-on, adaptive authentication, and phishing-resistant multifactor authentication
Automated identity provisioning, deprovisioning, access reviews, and certifications
One compromised admin account can take down an entire enterprise. We vault privileged credentials, enforce just-in-time access, and record every privileged session, from cloud consoles to mainframes.
What’s included
Credential vaulting and automatic rotation
Just-in-time and least-privilege enforcement
Privileged session monitoring, recording, and anomaly detection
Secrets management for DevOps pipelines and service accounts
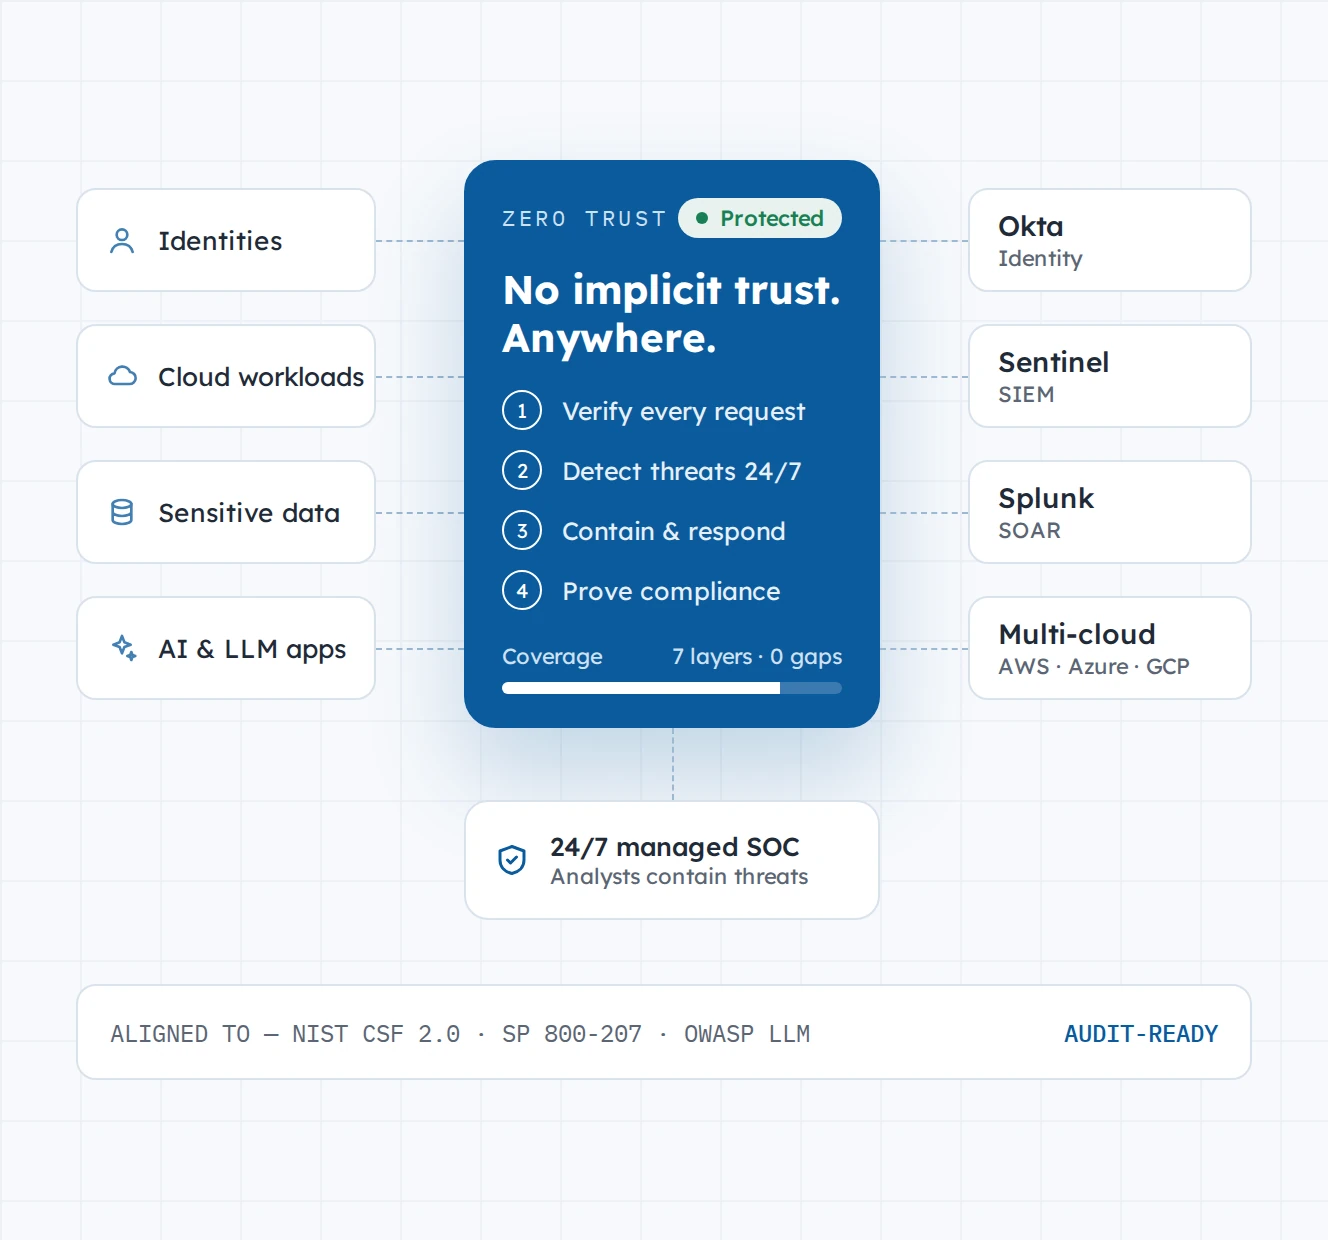
Design and implement Zero Trust architectures that evaluate access based on identity, device posture, context, and policy. We help enterprises reduce implicit trust and apply consistent access controls across users, workloads, networks, and applications.
What’s included
Zero Trust maturity assessment and phased roadmap
Micro-segmentation and Zero Trust Network Access (ZTNA) to replace legacy VPN
Device posture validation and context-aware access policies
Policy engine design, enforcement, and integration
Aligned toNIST SP 800-207CISA Zero Trust Maturity Model
AWS, Azure, Google Cloud, or all three. We give you one continuous view of posture, workloads, and identities, and we fix misconfigurations before attackers find them.
Improve threat visibility and incident handling by integrating security telemetry across endpoints, networks, cloud platforms, and identities. We help enterprises strengthen detection logic, prioritize alerts, investigate suspicious activity, and coordinate response procedures.
What’s included
24/7/365 Security Operations Center (SOC) monitoring and incident response, based on the agreed service model
Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) engineering on Splunk, Microsoft Sentinel, Google SecOps, and more
Endpoint Detection and Response (EDR) and Extended Detection and Response (XDR) deployment and tuning
Threat hunting and threat intelligence integration
Protect sensitive information throughout its lifecycle with controls that improve data visibility, access governance, and protection against unauthorized disclosure. We help enterprises apply data security policies across cloud platforms, SaaS applications, endpoints, and on-premises environments.
What’s included
Data discovery, classification, and Data Security Posture Management (DSPM)
Data loss prevention (DLP) across email, endpoint, and cloud environments
Encryption architecture and cryptographic key management strategy
Immutable backups and ransomware recovery planning
Address security risks across enterprise AI applications, large language models, and autonomous agents. We integrate security controls into AI development and deployment workflows to help manage data exposure, model interaction risks, and access to enterprise systems.
What’s included
AI application red teaming for prompt injection, jailbreaks, and data exfiltration
Guardrails, output validation, and secure Retrieval-Augmented Generation (RAG) architecture
Shadow AI governance and control for unapproved usage
Identity, permissions, and tool-access for Models and agents
Aligned toNIST AI RMFOWASP Top 10 for LLM Applications
Every program we deliver is built on eight non-negotiables.
Unified visibility
One risk view across identities, endpoints, cloud, network, and AI, not eight dashboards.
Enterprise-grade scale
Architectures built for hundreds of thousands of identities and millions of daily events.
AI-driven detection
Machine learning that separates real threats from noise, so analysts act on what matters.
Automated response
SOAR playbooks that isolate hosts, revoke sessions, and rotate keys in seconds.
Hybrid by design
Cloud, on-prem, and mainframe protected under one policy framework.
Vendor-agnostic
We recommend what fits and integrate what you already own.
Open architecture
API-first integrations with your IT service management (ITSM), DevOps, and data platforms.
Continuous compliance
Controls mapped to frameworks and evidence collected automatically, all year.
Compliance
Compliance, Built In. Audits, Handled.
We help enterprises align security controls, technical safeguards, and documentation with relevant regulatory and industry frameworks, including SOC 2, HIPAA, PCI DSS, CMMC, and FedRAMP. Control mapping, evidence management, and compliance workflows support audit preparation, demonstrate accountability, and help maintain ongoing compliance efforts.
A phased delivery process that aligns security priorities, implementation, and ongoing improvement with business and operational requirements.
01
Discover
See every risk
We inventory assets, identities, data flows, and controls, then score your exposure against NIST CSF 2.0.
02
Prioritize
Fix what matters first
You get a risk-ranked roadmap with effort, cost, and business impact for every initiative.
03
Architect
Design for the next five years
Target-state design for identity, cloud, data, and AI protection, reviewed with your leadership.
04
Implement
Deploy without disruption
Phased rollouts with parallel runs, change control, and rollback plans for every cutover.
05
Operate
Defend around the clock
24/7 monitoring, response, and continuous tuning under defined SLAs.
06
Optimize
Get stronger every quarter
Quarterly business reviews, maturity re-scoring, and roadmap updates as threats evolve.
Why AppsChopper
Engineering-Led Security. Accountable Delivery.
We combine security engineering, custom development, and systems integration to help enterprises implement security capabilities aligned with their technology environment. Our approach emphasizes practical execution, transparent ownership, and long-term maintainability.
It’s the strategy, engineering, and operations that protect a large organization’s identities, infrastructure, data, applications, and AI systems. It typically covers risk assessment, architecture, platform deployment, 24/7 monitoring, incident response, and compliance.
Assessments typically cost $15K–$50K. Implementation projects run $75K–$300K+, and managed 24/7 coverage starts at $8K–$15K per month. We provide a detailed estimate after a free discovery call.
Zero Trust is a model that verifies every user, device, and request continuously instead of trusting anything inside the network. If you run hybrid work, multi-cloud, or third-party access, it’s one of the most effective ways to limit breach impact.
Yes. We’re vendor-agnostic. We start by maximizing what you already own, integrate it into a single detection and response layer, and recommend new tools only when there’s a clear gap.
We red-team your models against prompt injection, jailbreaks, and data leakage, add guardrails and secure retrieval, govern shadow AI use, and align controls to the National Institute of Standards and Technology (NIST) AI Risk Management Framework (AI RMF) (NIST AI RMF) and Open Worldwide Application Security Project (OWASP) Top 10 for LLM Applications.
Yes. We map your controls to the framework, close the gaps, automate evidence collection, and support you through the audit.
Most engagements begin with a discovery call within a week. Assessment findings typically follow in a few weeks, depending on scope.
Yes. Managed clients get 24/7/365 monitoring and response, and we offer response retainers for organizations that want guaranteed response times.
Talk to Our Team
Strengthen Your Enterprise Security Strategy
Discuss your security priorities, technology environment, and business requirements with AppsChopper. Explore practical approaches to security engineering, integration, and modernization.
Discuss your enterprise security priorities
Explore relevant security capabilities and integrations
Identify potential next steps based on your requirements
Discuss Your Security Needs
Share a few details about your organization and security priorities. Our team will follow up to discuss your requirements.