Table of Contents
If your underwriting model hallucinated a risk factor today, would anyone catch it before the policy was bound?
AI hallucinations have become the go-to boogeyman in insurance risk conversations, and for good reason. When a model fabricates information, the consequences can ripple through claims, underwriting, and compliance in ways that are hard to unwind after the fact. However, treating every hallucination as equally dangerous is a mistake that leads to either paralysis or a false sense of security.
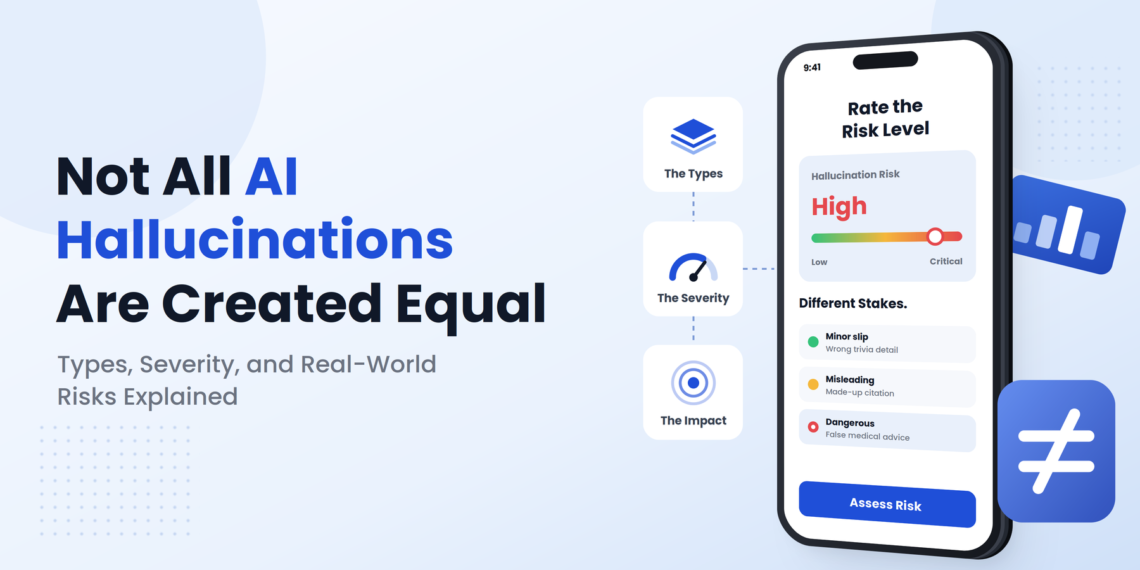
The truth behind AI hallucinations is much more nuanced. AI hallucinations in insurance are not all dangerous, except when they can invalidate a claim, misinterpret a policy, or trigger a regulatory examination.
The Spectrum of Risk
Not all hallucinations are created equal. A model that slightly rephrases a customer’s summary or generates a harmless internal note is not a quality issue. Rather, it is a governance crisis. Although these low-stakes errors are annoying, they do not necessarily put a business at risk.
The real danger lies in a narrow band of high-consequence outputs. For example, a claims model might fabricate a policy exclusion that doesn’t exist, effectively denying coverage the policyholder is entitled to. Another example is an underwriting assistant that misreads a risk factor and hallucinates a data point that shifts a premium calculation. Many people read these as stylistic hiccups. In reality, they are decisions with legal, financial, and reputational weight.
The most common mistake made by carriers is applying a single risk lens across every AI touchpoint. A hallucination in a marketing email draft and one in claims adjudication have vastly different consequences. Yet too many governance frameworks treat them as if they are in the same category of problem.
Why Tiering Matters More Than Elimination
In a perfect world, AI would not hallucinate at all. However, that expectation is unrealistic. Moreover, pursuing hallucinations uniformly wastes resources that should be focused where the stakes are highest. Ultimately, what insurance needs is a tiered governance model that aligns oversight with the level of consequence.
The most important action to take is to identify which workflows touch claims determinations, policy interpretation, or regulatory reporting. Then, insurers should build stronger verification, human review, and audit trails. It is also important to be honest about which workflows carry lower stakes and don’t require the same friction. A CIO or Chief Claims Officer who understands this distinction can allocate scrutiny effectively rather than spreading it thin or over-engineering controls on low-risk tools.
Building the Right Governance Map
Building the right governance map can be tricky for insurance organizations. It is easy to recognize that hallucinations are a risk. However, establishing a clear framework for classifying which systems need heavy guardrails versus light ones is difficult. Without the map, governance becomes reactive. Rather than building it after something goes wrong, it is more effective to design it proactively across the AI portfolio.
A mature approach starts taking an inventory of every AI touchpoint that influences claims, underwriting, or compliance outcomes. Then, there should be risk classification tied to real businessand regulatory consequences. Lastly, it is essential to have the right verification layers. This can range from
Where This Goes from Here
Insurance leaders don’t need to fear AI hallucinations, but they should stop treating all AI risk as the same. The organizations that are getting this right are the ones building governance around consequences, not capabilities.
If your team is working through how to map AI workflows by hallucination risk, AppsChopper can help. Reach out to AppsChopper to talk through a digital transformation strategy built around real risk tiers. That way, your AI investments strengthen your claims and complaints posture instead of exposing it.